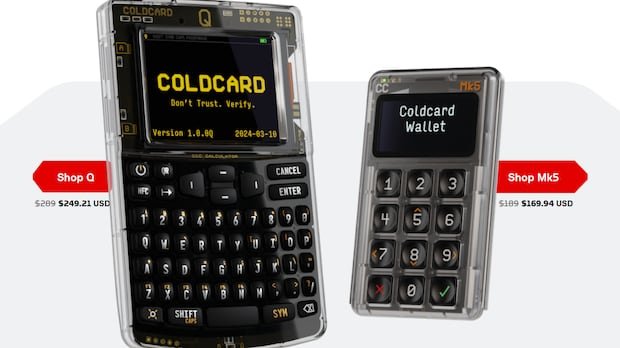

A recent data breach has targeted Coldcard, a bitcoin-only hardware wallet, resulting in hackers stealing over $100 million US worth of bitcoin from users’ wallets. The wallet, developed by Toronto-based company Coinkite, enhances security by storing “seed phrases” offline within the physical device, adding an extra layer of protection to the public blockchain network where bitcoins are stored.
The breach was caused by a software bug identified by Coinkite, enabling hackers to reconstruct wallet seed phrases remotely without needing physical access to the device. As a result, 1,596 bitcoins were stolen from approximately 7,300 addresses through three confirmed attack waves, with a potential loss of 2,055 bitcoins worth around $130 million US if a fourth wave is verified.
Coinkite has urged affected users to transfer their funds immediately and released firmware updates to address the issue. The company admitted the vulnerability originated in March 2021 due to a flawed random number generator in the firmware. Coinkite has halted shipments of devices with the vulnerable firmware and destroyed remaining inventory.
The ongoing investigation has shared details with U.S. law enforcement agencies, cryptocurrency exchanges, and cyber-investigation groups to track down the hackers. Security experts caution against keeping compromised bitcoin in affected wallets and recommend installing Coldcard’s latest firmware for enhanced protection, especially for new wallets created post-fix.
Coinkite is conducting a technical review, while experts emphasize the importance of migrating funds to safe addresses at custodian services or exchanges if users are uncertain about their wallet’s security. Despite the challenges posed by the breach, efforts are being made to recover funds and identify those responsible.